The most common mistakes and solutions for Swiss companies
The Swiss Federal Council adopted a report on digital sovereignty at the end of 2025, focusing on operational autonomy, control, and managing critical dependencies. For Swiss companies, the question is therefore less whether to use the cloud, but how to operate it in a way that ensures responsibility, security, and costs remain sustainably manageable.
Many Swiss companies confuse going live with their cloud platform with the actual goal. Once the migration is complete and all workloads are running, the expected benefits often fail to materialize: IT is not relieved, operations become increasingly complex, costs rise gradually, and security and compliance tasks are handled reactively. At the latest during an audit or an incident, it becomes clear what has been missing: clear responsibilities, robust processes, and governance that holds up in day-to-day operations.
These typical mistakes keep recurring – regardless of platform or provider:
-
Responsibility remains unclear
-
Costs are not managed as an operational process
-
Security is added as an afterthought
-
Monitoring without an actionable framework
-
Recovery is theoretical
-
Hybrid environments emerge as a byproduct
-
Lift-and-shift as a shortcut
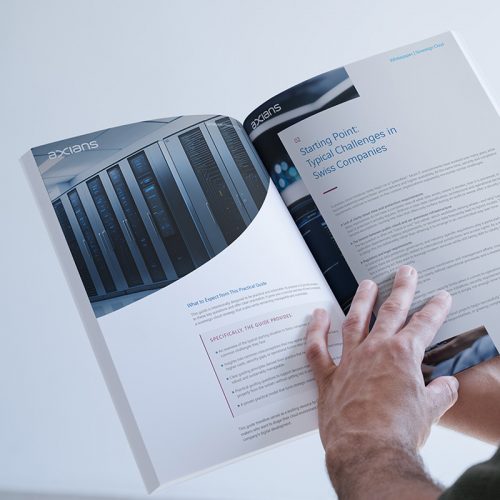
How to build your cloud infrastructure in a sovereign, secure, and controllable way – the ‘Sovereign Cloud’ practical guide from Axians provides concrete guiding principles, decision-making questions, and a proven approach model. Download the guide for free now.
Operational model as a key success factor – enabling cloud to deliver impact
Most problems arise because it is not clearly defined how a cloud platform is operated. An operating model establishes exactly this clarity and accountability in the following areas:
Governance & responsibilities (service boundaries, RACI, escalation paths)
- Who is responsible for operations, change management, security controls, and incident response?
- Which responsibilities lie with the provider, which with the partner, and which remain in-house?
- How are decisions and escalations handled in a crisis, with clearly defined roles and points of contact?
FinOps: treating cost control as an operational discipline
- Transparency (tagging/allocation, cost centers, showback/chargeback)”
- Rules for usage and scaling (budgets, guardrails, approvals)
- Continuous optimization (rightsizing, storage and lifecycle policies, reservations, licensing logic)
Security & Compliance: by design, verifiable in operations
- IAM & access control (MFA, roles, least privilege, access recertifications)
- Logging/monitoring and auditable controls
- Configuration and patch standards, vulnerability management
- Evidence: documented processes, clear responsibilities, and auditable execution.
Monitoring, incident processes, and resilience (when it matters most)
- SLIs/SLOs and clearly defined thresholds instead of “alert fatigue”
- Runbooks/playbooks, defined incident roles, and clear communication channels
- Backup & recovery with clearly defined objectives (RPO/RTO) and regular restore testing
How Axians supports
From roadmap to implementation with Axians
Anyone looking to implement this operating model in their own cloud environment does not need another ‘cloud plan’, but a clear framework for action: first, a baseline assessment focusing on data, dependencies, and risks; then deriving a target operating model (governance, FinOps, security, monitoring/resilience); followed by iterative implementation and continuous operational optimization.
This is exactly where Axians positions itself: as a partner that supports cloud and hybrid environments in a structured way – from assessment to implementation through to reliable operations – drawing on experience and expertise in the Swiss market, including Swiss cloud and managed IT components, managed operations and support, as well as integrated security and cost management
ANDREAS WENGER
Presales Engineer, Axians Amanox