Discover how we offer a structured and effective approach to managing risks systematically.
A guide to mitigating hidden risks and securing your future success
Find out more about effective third-party risk management and the importance of implementing a comprehensive framework. Download our white paper for in-depth insights and valuable tips.
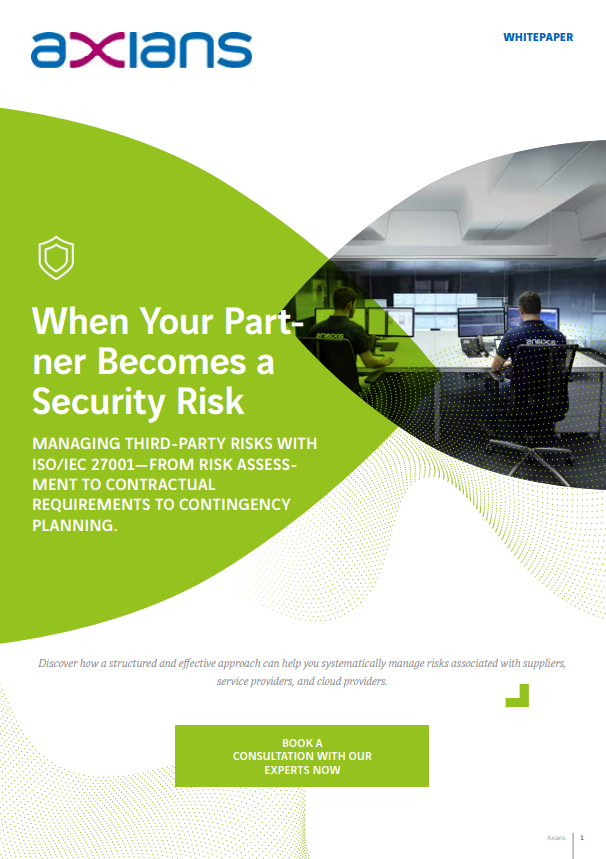
Find out more about effective third-party risk management and the importance of implementing a comprehensive framework.
In this white paper, you’ll learn:
- Recognizing third-party risks: Identify and systematically assess security risks posed by suppliers, IT service providers, and cloud providers at an early stage.
- Structured risk management: Classify third parties according to their business criticality and define appropriate protective measures based on ISO/IEC 27001:2022.
- Clear Security Requirements: Establish contractual requirements regarding data protection, access rights, security controls, and reporting obligations.
- Continuous Monitoring: Verify security standards through regular risk assessments, audits, and certification evidence.
- Preparation for Security Incidents: Ensure the ability to respond to outages or cyberattacks through defined responsibilities, reporting processes, and emergency plans.
- Transparency and business continuity: Integrate third-party risks into the ISMS, manage dependencies in a targeted manner, and minimize potential impacts on business operations.
This white paper is free for you! Take advantage of this opportunity and learn more about effective third-party risk management.